Every year someone declares the password dead — and every year billions of logins still depend on one.
Until passkeys finish taking over, password strength remains one of the highest-leverage security decisions you make. And most advice about it is outdated.
Key takeaways
- Length beats complexity: 16+ characters is the target.
- Never reuse a password — reuse converts one breach into many.
- Rotate on evidence of compromise, not on a calendar (current NIST guidance).
How passwords actually get broken
Attackers rarely sit guessing at a login form. They take leaked databases and crack them offline with GPU rigs testing billions of combinations per second — or simply replay passwords from one breach against other services.
Both attacks exploit the same two habits: short passwords and reused passwords.
Length beats cleverness
“P@ssw0rd!” satisfies every complexity rule and falls instantly — crackers try predictable substitutions first. Each additional character multiplies the search space far more than any symbol swap.
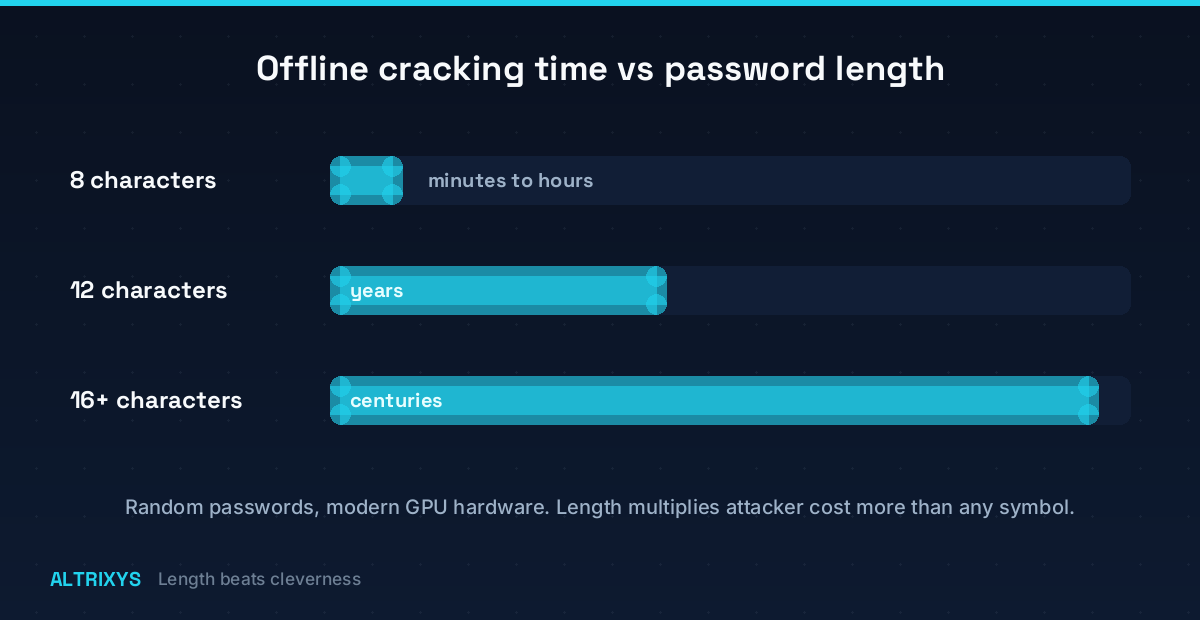
A 16+ character passphrase of random words — correct-horse-battery-staple style — is both stronger and easier to remember than “Tr0ub4dor&3”.
Length is the primary defense — every character multiplies the attacker’s cost.
Let a password manager do the work
The realistic way to hold hundreds of unique, long passwords is not memory — it is a reputable password manager. You remember one strong master passphrase; the manager generates and fills the rest.
Bonus: managers quietly resist phishing — they refuse to autofill credentials on look-alike domains that fool human eyes.
MFA and passkeys: the road ahead
MFA means a stolen password alone is not enough — enable it everywhere, preferring authenticator apps or hardware keys. Passkeys go further: device-bound cryptographic keys that cannot be phished or leaked in a database breach.
Adopt passkeys where offered — and keep password hygiene strong for the long tail of services still living in the password era.
Altrixys provides authorized penetration testing, security hardening and compliance services from Athens, Greece. Want to know how your organization would hold up against a real attack? Request a free assessment.